One layer for the web-based desktop
The web used to live in the browser.
Now it’s everywhere.
- Browsers
- Desktop apps
- AI
- Messaging
- Meetings
- The next tool
For security teams, the chase never ends.
THE CHALLENGE
New tools. Many surfaces. Limited coverage
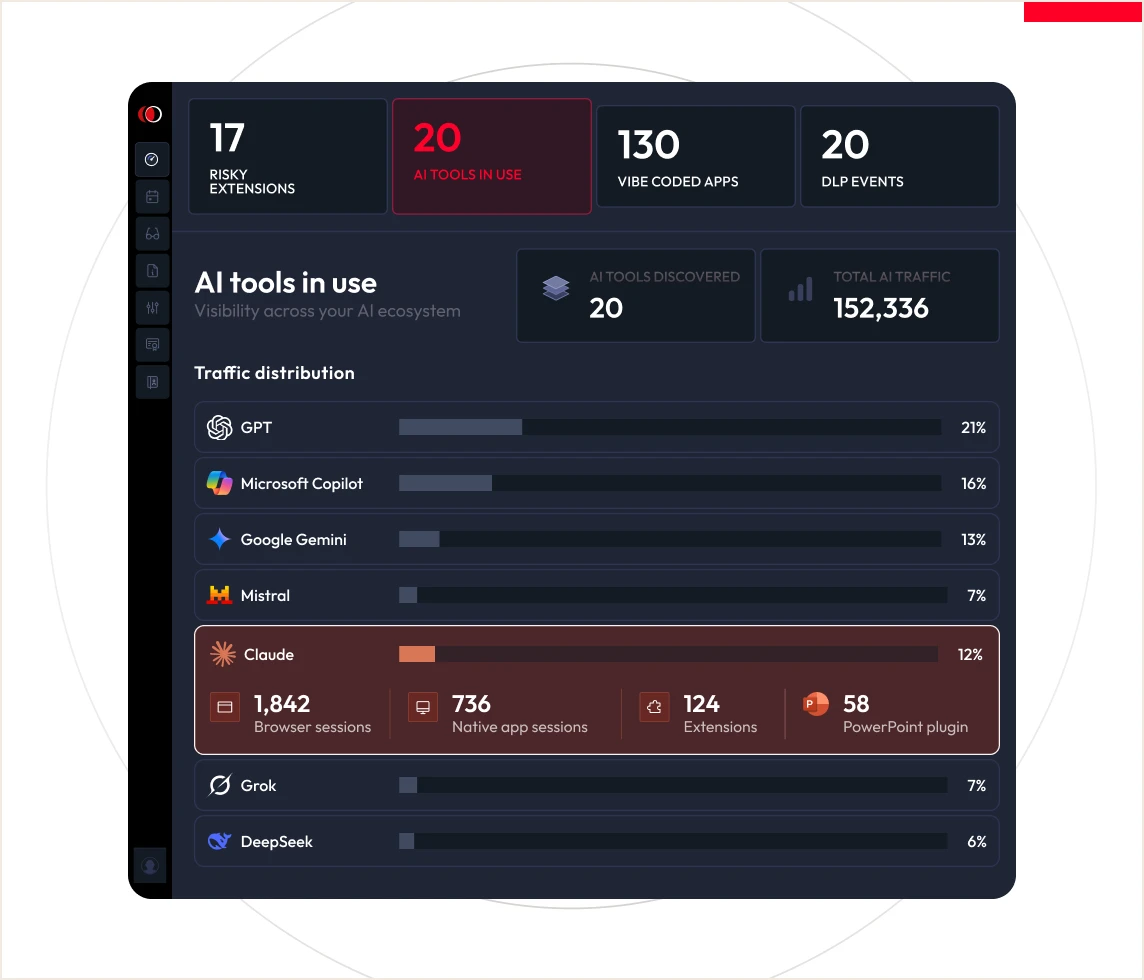
Take Claude, for example. Your users can access it through browsers, extensions, desktop apps, embedded workflows, PowerPoint, and other desktop surfaces.
Each creates a new surface your team needs to secure – including
prompts, links, attachments, identities, and context.
WHAT RED ACCESS GIVES ME
Instead of chasing every tool and surface,
Red Access protects work wherever it
happens
And when the next tool shows up tomorrow, you don’t start over. You already have:


More tools. More Surfaces. More blind spots
Work keeps reshaping across Desktop apps, AI Tools, Browsers, Meetings, and Messaging.
Red Access brings them together, unifies visibility and intent, and identifies what’s being used and risky activity across all surfaces.
Context without the homework
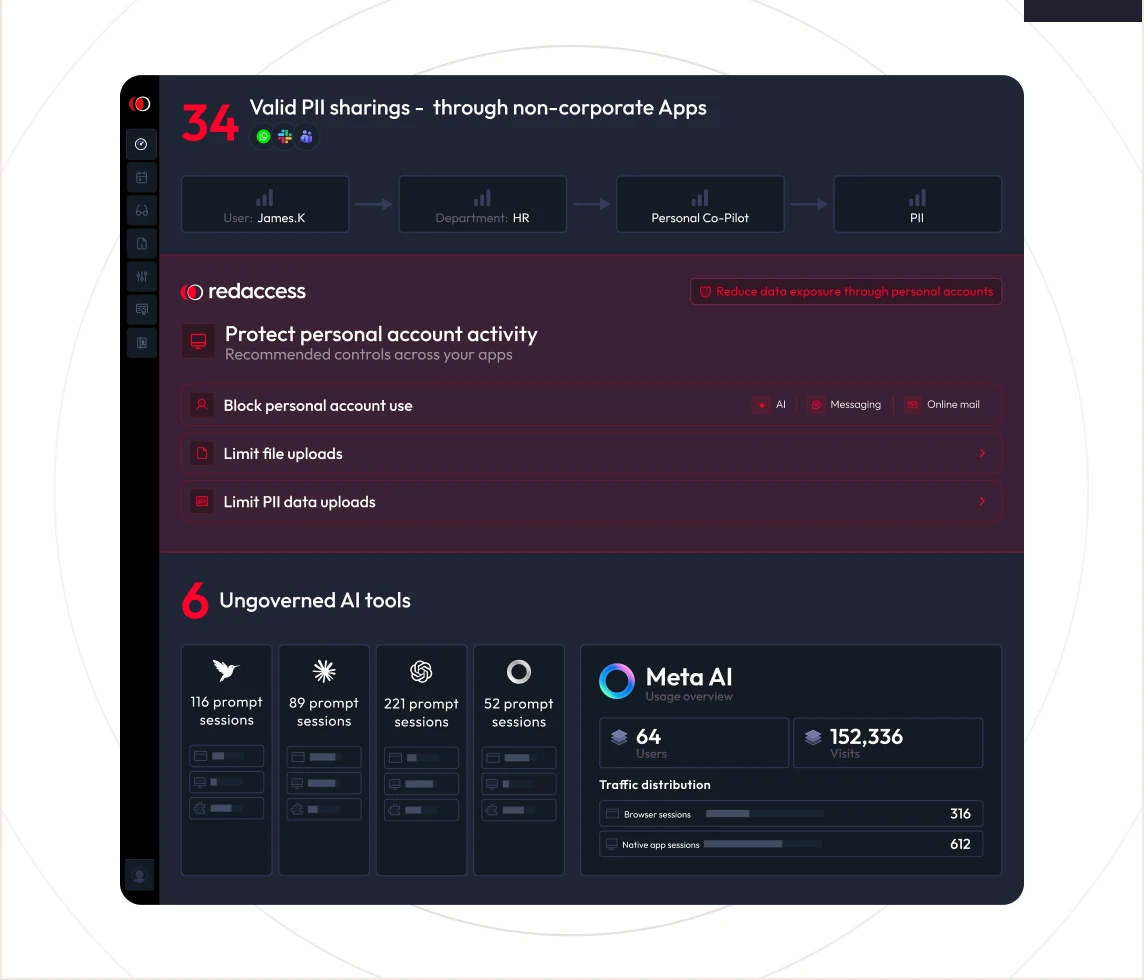
Security teams need answers and priorities without spending hours piecing information together.
Red Access turns activity into clear, accurate answers—what’s risky, why it matters, and what to fix first.
Security that reaches the activity inside
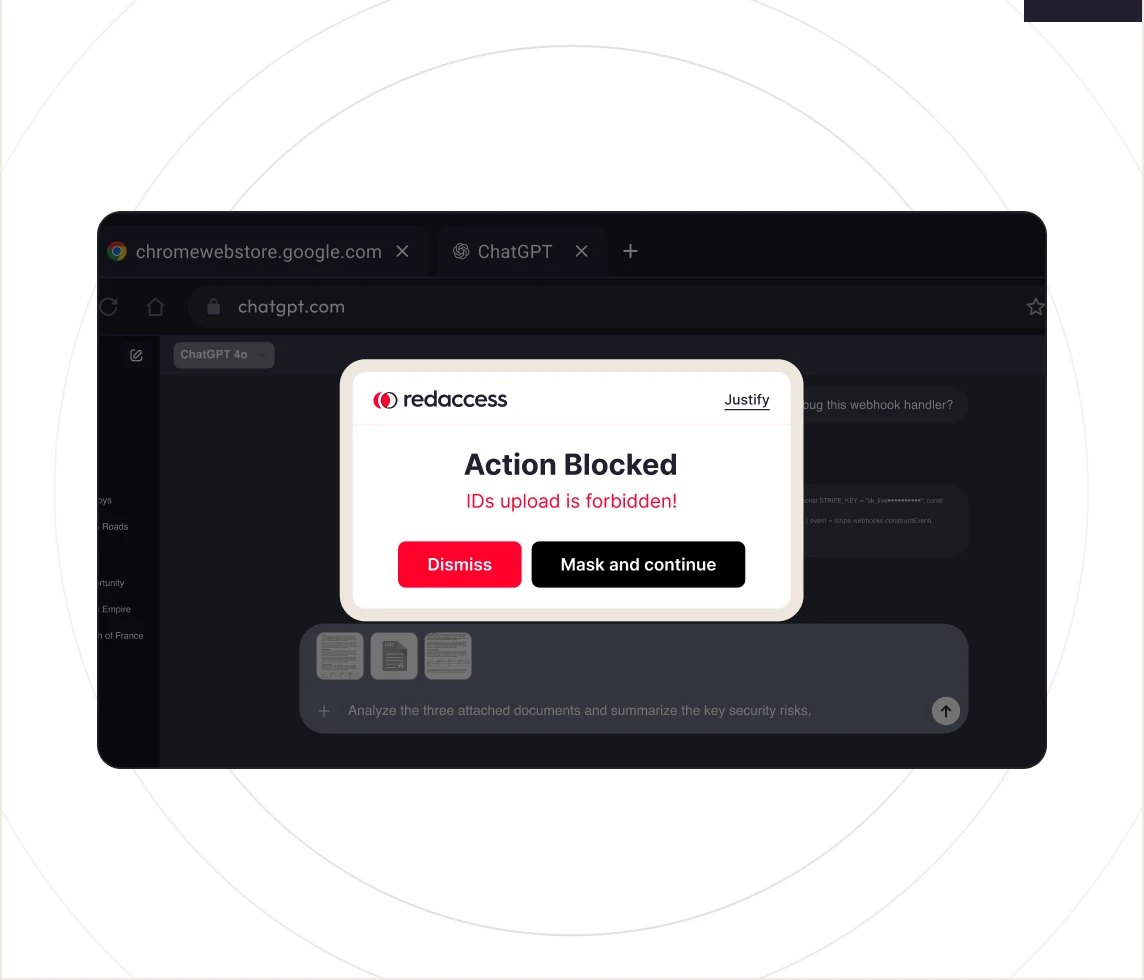
Securing links, files, data, prompts, and accounts across all desktop apps, AI tools, and browsers takes multiple tools -with uneven depth, different policies, and gaps in coverage.
Red Access protects activity inside each session in real time – stopping data leaks, malicious links and files, and risky user activity across every surface.
How it works
Open the app. Red Access loads with the session.
For agentless, app-agnostic, local analysis and coverage.
Configure once
Set Red Access once at the OS / environment level via MDM, GPO, a package manager, etc.
The app opens
The user opens a web-based desktop app such as Chrome, Edge, Slack, Teams, Claude Desktop, Microsoft 365, embedded webviews, and more.
Red Access loads with the session
The security engine loads seamlessly as a resource, bringing policy and context directly into the session.
Real-time control and context
Controls are applied and policy is enforced locally, while management, intelligence, and reporting stay centralized in the Red Access cloud.


A Different Security Layer
Cover the session without inheriting the limitations of the tools around it.
Desktop Al apps (prompts, account, and context)
Red Access

Yes
SASE/SSE

No
Enterprise Browser
No
Browser Extension
No
Desktop messaging/meeting apps
Red Access
Yes
SASE/SSE
No
Enterprise Browser
No
Browser Extension
No
User experience
Red Access
Seamless. Flexible across tools, surfaces, and behaviours
SASE/SSE

Proxying all traffic
Heavy latency
Website breakage
Enterprise Browser
Behavioral change
Browser Extension
Chasing browsers & surfaces
Market experience
Red Access
Coverage Simplicity Depth
SASE/SSE
Complex, heavy, expensive
Enterprise Browser
Constant friction with users; limited coverage by design
Browser Extension
Easy to bypass; limited coverage; sufficient for basic needs
Requires an agent?
Red Access
No
SASE/SSE
Yes
Enterprise Browser
Yes
Browser Extension
Yes
Browser-agnostic
Red Access
Yes
SASE/SSE
Limited – some surfaces/
protocols are out of scope (WSS, pinning,etc.)
Enterprise Browser
No
Browser Extension
Limited – specific support required
Covers headless and embedded browsers
Red Access
Yes
SASE/SSE
Yes
Enterprise Browser
No
Browser Extension
No
Fits the stack you already run
Add the missing layer. Don’t replace the stack.
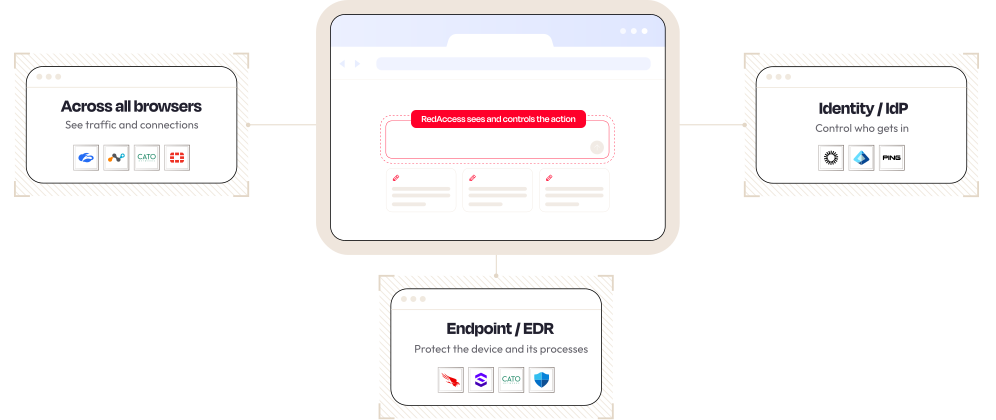
Configuration
A one-time network setting at the OS level
Your desktop apps, browsers, AI tools, messaging, meetings, Office, and plugins are all covered out of the box.

No endpoint agent

No browser extension

No enterprise browser rollout
Natively integrated
Works with the tools you already use
Add session context to your existing stack and environments.
01
SIEM
Integrate logs, reports, and events with your SIEM (cloud or on-prem).
02
Identity providers
Sync your existing identities, groups, and policies.
03
Security stack
DLP (Microsoft Purview, etc.), firewall (Palo Alto, Fortinet, etc.), SASE (Zscaler, Netskope, etc.), VDI (Citrix, Horizon, AWS, etc.)
04
Servers and VDI
Terminals, servers, VDI (including non-persistent environments), and complex environments.
Seamlessly integrated into your existing security stack:



and many more
Trusted by security leaders

Chris Detert
IT Director, USA Swimming

Red Access delivers meaningful risk reduction and continues to add value through ongoing product enhancements. They gave us greater visibility into browsers, extensions, Shadow AI, and DLP risks.
Joe Damian
Senior Director IT, Franklin Empire
Adding Red Access as another layer of security helped us eliminate risky user behavior – get Red Access and have your head clear.

Eitan Israelov
Director IT and Security, RIMEX
Red Access turns every app into a manageable security layer – blocking threats and reducing data exposure without disrupting how employees work.
Market Recognition