Red Access Wins Globee Award for Innovation, Named Gold Winner and Best of Category for Cybersecurity Product of the Year


Protect work across browsers, AI, messaging, and more

Securing browser activity

Enterprise Browser Alternative
Protection Without Friction
STOP
THE CHASE


Safe Browsing with Red Access

Red Access Data Loss Prevention (DLP)

Red Access Browser Extension Protection

Red Access SaaS Security

Secure Contractor & BYOD Remote Access

Adopt cutting-edge technologies like WebView2 without sacrificing security

Control GenAI Use Without Blocking Innovation

Streamlined, frictionless web security

Stop credential theft and spoofed sites in real time

SSE Security Without Replacement

Govern Vibe-Coded Apps
STOP
THE CHASE

Lorem ipsum dolor sit amet,
consectetur

Lorem ipsum dolor sit amet,
consectetur

Lorem ipsum dolor sit amet,
consectetur

Lorem ipsum dolor sit amet,
consectetur

Lorem ipsum dolor sit amet,
consectetur
Lorem ipsum dolor sit amet,
consectetur
STOP
THE CHASE
USe case
Stop credential theft and spoofed sites in real time.
Red Access protects from modern phishing attacks by going deep into the session, rather than staying at gateway-level. Our agentless platform monitors and analyzes page behavior and user actions in real-time, blocking credential misuse and cookie theft while keeping the user experience unchanged.
The web browser has become the world’s most important application, serving as the new “operating system” for the digital enterprise. This browser-centric reality drives new productivity, but also creates visibility gaps and security blind spots:


features
Network tools and email security don’t see what happens in the browser—Red Access does.
Until now, organizations had limited options: heavyweight SSE that demands full network migration and enterprise browsers that only secure themselves. Organizations need both, but cannot afford the network overhaul or adding multiple tools to their stack.
01


Catch threats at the source. Red Access continuously analyzes live pages and detects impersonation attempts with advanced behavior and DOM heuristics.
02

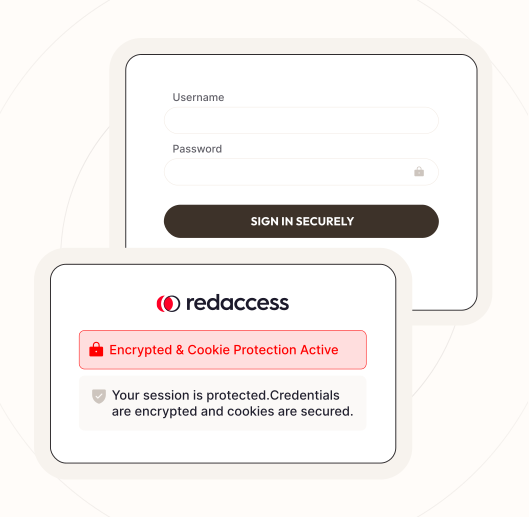
Identities are kept safe by binding credentials to approved domains and applications. Login attempts on an unknown or malicious domain are automatically blocked, while cookies and session tokens are secured against theft or misuse.
03

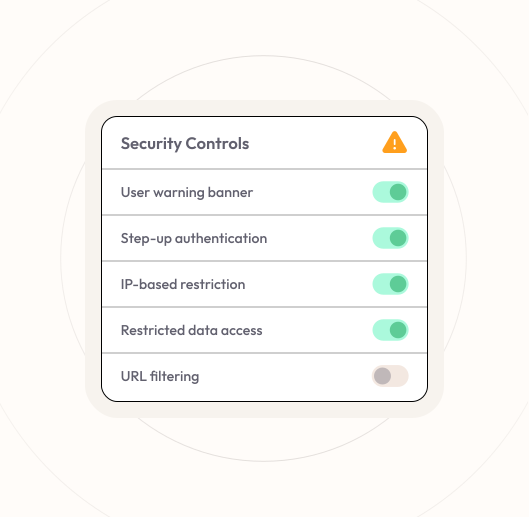
Always-on awareness continuously flags risks, while teams can choose between diverse security controls that adapt to risk:
04

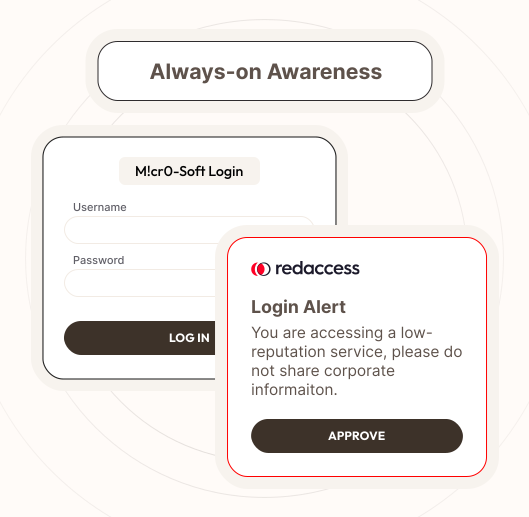
Not every scenario requires a hard stop. Ensure user productivity with policies that can dynamically block, warn, or allow with restrictions, based on user identity, device posture, application sensitivity, and real-time risk level.
05

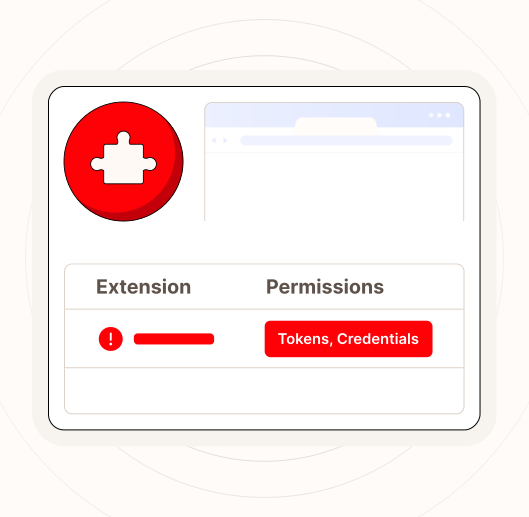
Attackers don’t stop at the browsing session. Red Access protection extends to phishing attempts through browser extensions that attempt to gain excessive permissions, access sensitive data and exfiltrate information.
06

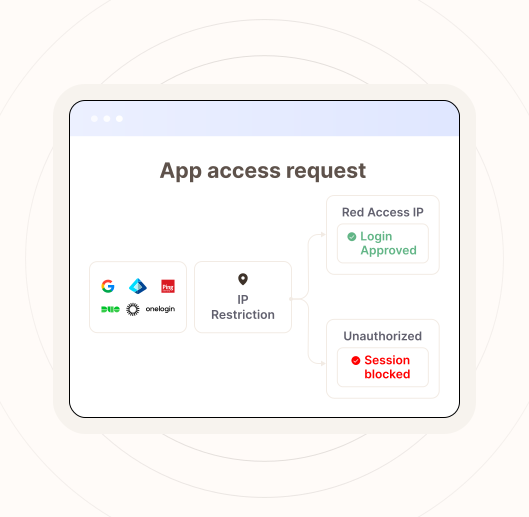
Limit access and prevent impersonation with anti-impersonation checks, advanced IP-level restrictions, and conditional access. Okta integrations ensure sessions are approved with the right context and without leaving apps exposed to open access.
red access

Firewalls
Supercharged to SSE-grade protection

SSO and IdPs,
SAML Support

SIEM
& API

Active Directory
(Local & Cloud)

Customizable Brand and User Experience
testimonials

One of our biggest challenges was users clicking on links and attachments in emails. By adding Red Access as another layer of security, we were able to protect against those threats and reduce risky user behavior.
Joe Damian
Senior IT Director, Franklin Empire
discover the new sse
